Explanation of the Current Alert Level of ELEVATED
The alert level is the overall current threat level.
This level is based on analysis by the Center for Internet Security® (CIS®) Security Operations and Intelligence (SO&I) division covering the cyber threat landscape for Quarter 3 (Q3) of 2026. In calendar year 2026Q3, SO&I published 43 cybersecurity advisories including 12 advisories where vulnerabilities are being exploited in the wild. SO&I received an increase in SLTT reported incidents that resulted in finished intelligence products and Iran targeted internet facing operational technology devices in the U.S. water and wastewater sector. Organizations and users are advised to update and apply all appropriate vendor security patches to vulnerable systems and to continue to update their antimalware detections daily. Organizations should also provide updated user awareness training on malicious attachments and links contained in emails especially from un-trusted sources.
Vulnerability Advisories
Latest Advisory
Centralize Your Vulnerability Awareness
Keep track of new vulnerabilities in a centralized location to prioritize your remediation tasks and advance your efforts to achieve essential cyber hygiene through CIS Critical Security Controls: Implementation Group 1 (IG1).
Resources for Countering Cybersecurity Threats
Top Malware
During the first half (H1) of 2026, PureLogs led the Top 10 Malware list of the Multi-State Information Sharing and Analysis Center® (MS-ISAC®), comprising 27% of detections by MS-ISAC monitoring services. Agent Tesla, a remote access trojan, and CoinMiner, a cryptocurrency miner, followed PureLogs.
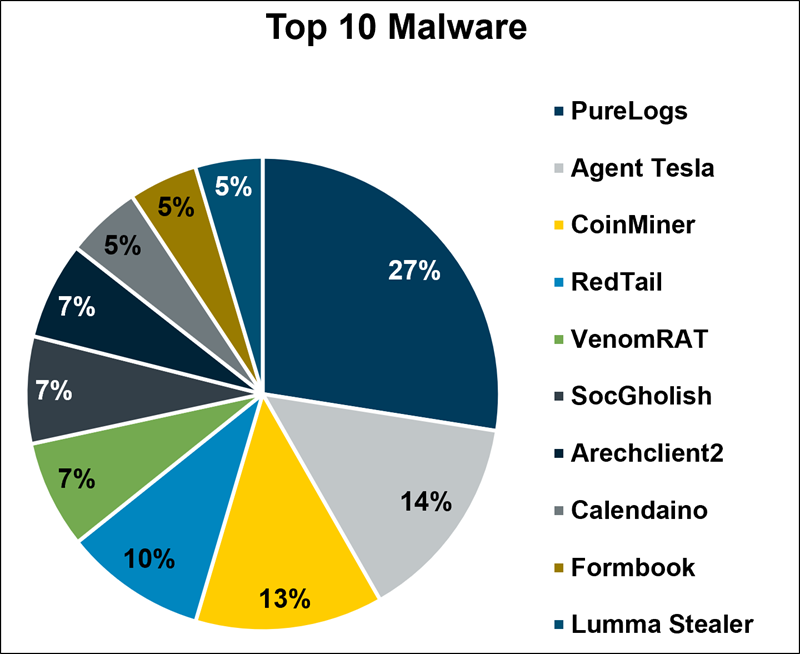
In H1 2026, the MS-ISAC also observed the return of Lumma Stealer, an infostealer malware, while PureLogs, RedTail, and FormBook made their first appearances.
- PureLogs is a .NET infostealer from the Pure family of malware. Delivered via phishing (TXZ archives) using the PawsRunner steganography loader, PureLogs steals credentials, cookies, and browser data from 100+ applications.
- RedTail is a Linux cryptojacker that mines Monero cryptocurrency. First observed in early 2024, the malware obtains initial access via SSH brute-force or exploitation (PAN-OS, PHP, others), and it achieves persistence via implanted SSH keys. RedTail evades detection through file and log deletion.
- FormBook is a Windows infostealer / Malware as a Service (MaaS) offering delivered via phishing emails. Using fileless execution via process hollowing into signed Windows binaries, FormBook steals credentials, cookies, keystrokes, and clipboard from 40+ browsers and email clients.